
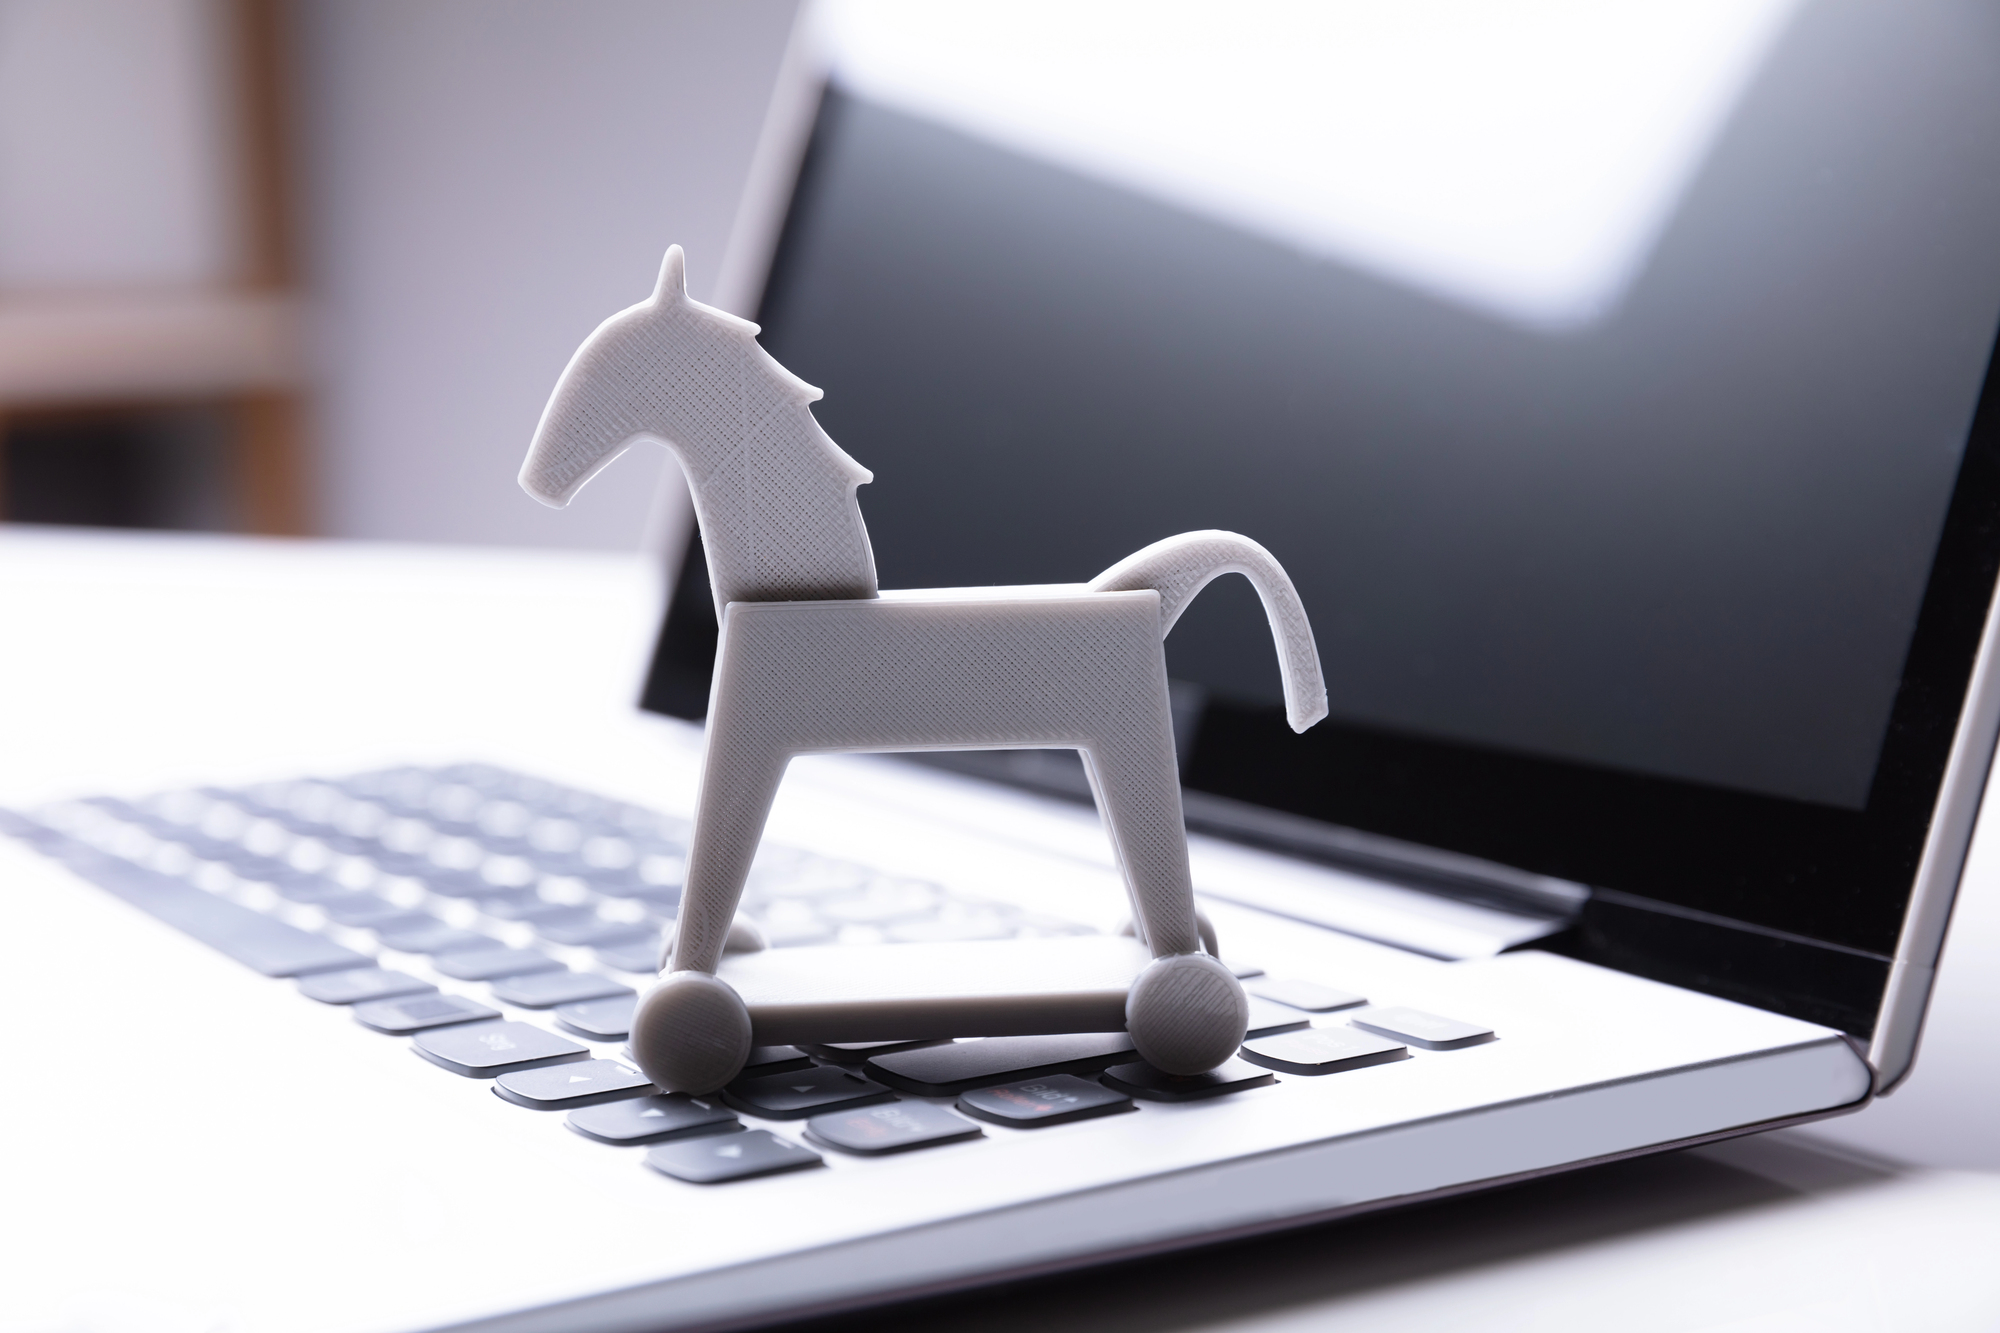

A trojan virus represents a deceptive type of malware that tricks users into thinking it is legitimate software before they download it. Named after the mythical wooden horse, this malicious code manages to infiltrate systems by masking its true intentions. Once inside, it can compromise your device, steal sensitive data, and create severe security risks for everyday computer users.
Definition of Trojan Horse Virus
A trojan horse virus is a specific malicious program that disguises itself as a helpful application or file to deceive unsuspecting victims. Unlike standard computer worms, these threats cannot replicate themselves independently. Instead, they rely heavily on social engineering tactics, convincing individuals to execute the harmful file voluntarily and thereby initiate the dangerous infection process.
How Trojan Viruses Differ from Other Malware
Many people confuse this threat with a traditional virus, but trojans operate differently because they do not spread by attaching themselves to host files. While standard malware focuses on aggressive propagation across networks, a trojan relies on deception. It often arrives hidden inside an email attachment or bundled with free software, waiting patiently for the user to activate it.
Common Characteristics of Trojans
These malicious entities are specifically designed to go undetected by hiding their true payload behind a harmless facade. A typical trojan infection often establishes a hidden backdoor, allowing an external attacker to gain remote access to the affected system. This unauthorized entry permits cyber criminals to monitor user activities, harvest private passwords, and deploy additional threats without immediate detection.
Types of Trojan Viruses
Backdoor Trojans
A backdoor trojan is a particularly dangerous type of malware that creates a hidden vulnerability within your operating system, allowing a remote attacker to gain complete control over the compromised machine. Once the malicious code manages to infiltrate the device, it establishes a secretive command-and-control channel. This unauthorized remote access enables cyber criminals to execute commands, download additional harmful payloads, spy on user activities, and harvest sensitive credentials without the victim ever realizing their system security has been fully breached.
Banking Trojans

Banking Trojans are specialized malicious programs meticulously engineered to steal financial data, including online banking credentials, credit card numbers, and confidential passwords. When a user attempts to access financial services, this insidious malware may deploy deceptive pop-up windows or use keylogging techniques to capture private information. Financial institutions and everyday consumers rely heavily on advanced antivirus software and robust endpoint security measures to detect and prevent the trojan from successfully intercepting sensitive economic transactions.
Ransomware Trojans
Ransomware trojans represent a destructive threat that enters a system disguised as a harmless email attachment or a cracked software download. Once executed, the malicious code rapidly encrypts critical files and locks the victim out of their own device. The attacker then demands a substantial monetary payment in exchange for the decryption key. Maintaining secure backups, avoiding unfamiliar links, and deploying reputable security software are essential strategies to mitigate the severe risks associated with this aggressive digital extortion.
Detecting a Trojan Virus
Signs Your Device May Be Infected
Identifying an active trojan infection often requires paying close attention to unusual computer behavior and system anomalies. When malicious code operates silently in the background, it may establish a secret command-and-control connection that consumes excessive bandwidth and slows down your machine. Users should carefully monitor for any sudden performance drops, unexpected program crashes, or a strange pop-up appearing frequently, as these symptoms frequently indicate that an unauthorized attacker has managed to infiltrate the hardware.
Tools to Detect a Trojan Virus
To successfully detect a trojan virus and protect your personal data, utilizing advanced antivirus software and comprehensive endpoint security solutions is mandatory. These specialized programs catch any type of malware before it can cause widespread damage by performing key security functions, such as:
- Scanning files
- Inspecting incoming email attachments
- Monitoring network traffic
Cybersecurity experts always recommend downloading applications exclusively from trusted sources and running regular system scans to ensure that no hidden threats or dormant malicious payloads remain active on your computer.
How Trojans Can Go Undetected
Many variants of trojans are specifically engineered to go undetected for long periods by camouflaging themselves as legitimate programs or harmless system updates. By employing advanced evasion techniques, the malicious software manages to bypass standard security filters and avoid immediate detection by traditional scanners. Because these threats rely on careful social engineering and clever disguise, users must remain constantly vigilant, avoiding unfamiliar links and relying on multi-layered defenses to maintain absolute digital safety.
Removal Tips for Trojan Viruses
Steps to Remove a Trojan Virus
When you discover an active threat on your system, executing immediate removal steps is critical to stop a malicious code from causing further damage. To effectively secure your device, follow these essential steps:
- Disconnect your machine from the internet to sever any active command-and-control communication used by the attacker.
- Run a comprehensive scan using reliable antivirus software to identify and quarantine the trojan viruses.
Thoroughly cleaning your operating system helps eliminate any lingering backdoor vulnerabilities and restores device stability.
Preventive Measures Against Future Infections
Proactive defense strategies play a vital role in shielding your hardware from future digital threats and avoiding another dangerous trojan infection. To protect your systems effectively, you should consider the following best practices:
- Cultivate safe browsing habits, carefully scrutinize every email attachment, and steer clear of unfamiliar websites that might host harmful payloads.
- Implement strict endpoint security policies and educate employees about social engineering tactics to ensure unauthorized intruders cannot easily exploit system weaknesses or compromise personal data.
Importance of Regular Software Updates
Keeping your operating system and installed applications fully updated is a fundamental practice to block security exploits and patch critical software vulnerabilities. Cyber criminals frequently target outdated programs to infiltrate machines and deploy hidden malware. By scheduling automatic updates and maintaining robust security software, you significantly enhance your ability to detect anomalies, protect every credential, and ensure that malicious intruders fail in their attempts to breach your digital environment.